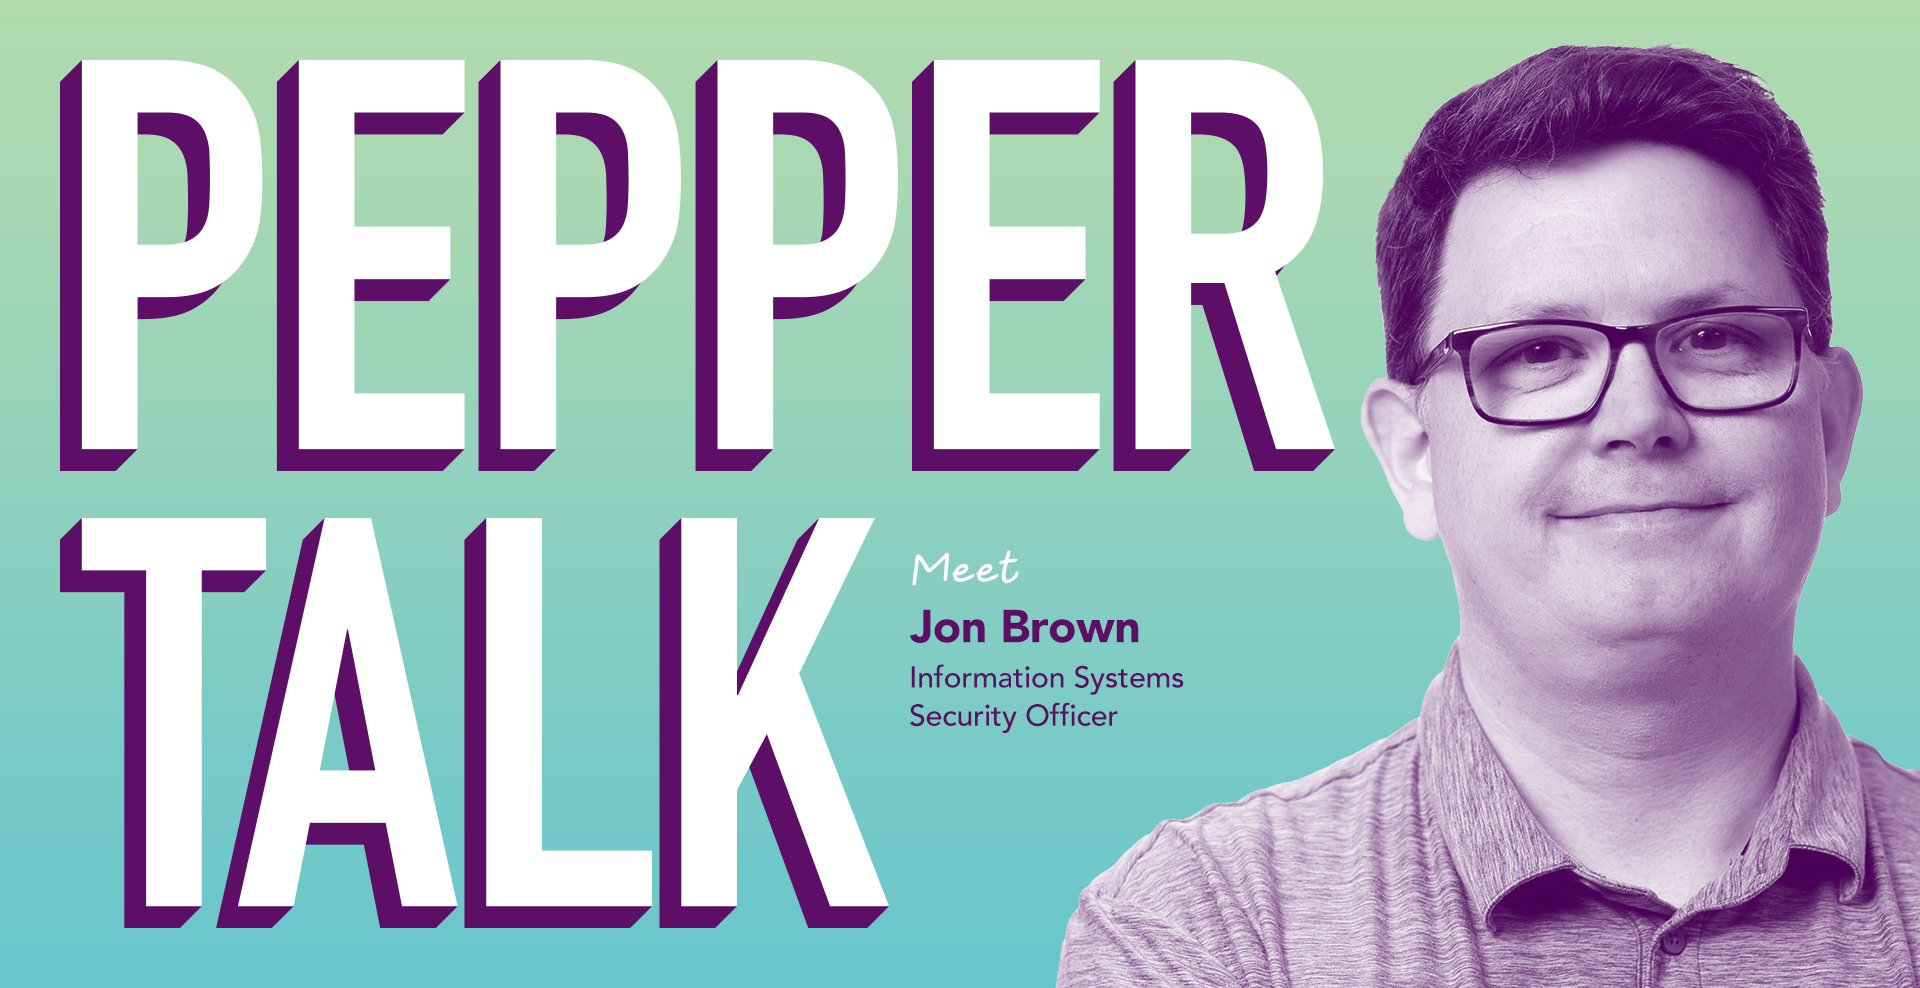
Pepper Talk with Jon Brown
Just a little background before we get started, Jon is our fearless Information Systems Security Officer. He’s worked with Eleven Peppers for years but has been an official part of our pepper family for over one.
1. Do you have any nicknames?
Jonathan is my full legal name, so always chose to shorten it. My history teachers all had fun with the name.
2. What is the first thing you do when you wake up?
Email, coffee, making breakfast, and getting my son out the door and on the bus with news in the background.
3. What part of protecting systems and data feels most rewarding to you?
What I find most rewarding is creating an environment where IT and security almost become invisible. In a well-run environment, people might wonder, “What does the IT guy actually do? I never see him dealing with outages or major issues.” To me, that’s a sign of success. Good IT isn’t about constantly reacting to problems or being the hero who puts out fires; it’s about anticipating problems, reducing risk, and building systems that are secure, reliable, and resilient enough that those fires rarely happen in the first place. Protecting systems and data is rewarding because when it’s done well, everyone else can simply do their jobs without having to think about it.
4. How did you get started in this industry?
I went to school for Graphic Design and Computer Animation and graduated back in 2001. I was the person in my class that became the computer lab monitor and eventually the go-to in class “my computer froze – guy”, so really found helping people rewarding and natural. Shortly after that got into teaching, and after a few bad experiences working in the design industry decided that I preferred helping people vs making text scroll and blink and the rest is history!
5. What security tools make your life easier and which ones slow you down?
JAMF our primary automation tool allows me to keep a pulse on what is happening with our fleet of workstations and is invaluable especially JAMF Protect and JAMF Security cloud. Our vulnerability tools always keep us on our toes though because security notices and alerts are posted daily, so just when you get through one batch of security concerns here comes another open 1000 issues to fix and the cycle continues.
6. What’s your first move when you’re handed a new system to secure?
Absolutely two things. First, I validate the use case. Some of the biggest risks come from systems or functionality that businesses don’t actually need, don’t use, or don’t fully understand the security implications of. Before securing something, I want to understand why we have it, what we need it to do, what data it touches, and just as importantly, what we don’t need it to do. Reducing unnecessary functionality and exposure is one of the simplest ways to reduce risk.
Second, I make sure the system is integrated into our Security Operations Center, including getting the appropriate security and audit logs into our Security Information and Event Management (SIEM) platform. That gives us visibility into what the system is doing and allows us to detect, investigate, and respond to suspicious activity. You can put all the right controls around a system, but if you can’t see what’s happening inside it, you’re still operating with a significant blind spot.
7. Rapid-Fire Round:
Caffeine or no? A MUST!
Sweet or savory? Sweet
Favorite TV series or movie? Burn Notice
Favorite place to travel? South East Asia (anywhere)
Hobbies? Collecting old Apple computers, writing apps for iOS, and Legos with my son
8. OK, admission time… If you could claim credit for one security architecture or framework, which would it be?
The work done by the MacOS Security Compliance Project is epic. Currently all Apple ecosystems in the world is being secured by this open-source project that came out of NIST. It’s published by Apple as the primary method for securing their own ecosystem and an invaluable tool for any company with Apple computers.
Thanks for meeting Jon. Stay tuned for our next interview with one of our Peppers.